
vCISOs
Clients want to feel secure, and insurers want proof. Map each client to a framework, assess the risk, collect the evidence and write reports insurers accept.
- Map each client to a framework such as NIST CSF or CIS Controls.
- Run risk assessments and keep evidence for every control.
- Write reports a cyber insurer or an auditor will accept.
The Problems This Job Actually Has
A framework the client cannot afford
Choosing the one an insurer accepts and a small business can carry.
Assessments that produce a PDF and nothing else
The finding that turns into a funded change.
Evidence that is a screenshot
Controls proven by records rather than by a picture of a setting.
The insurance questionnaire
The questions, the answers that hold up, and the ones that end cover.
Featured Template
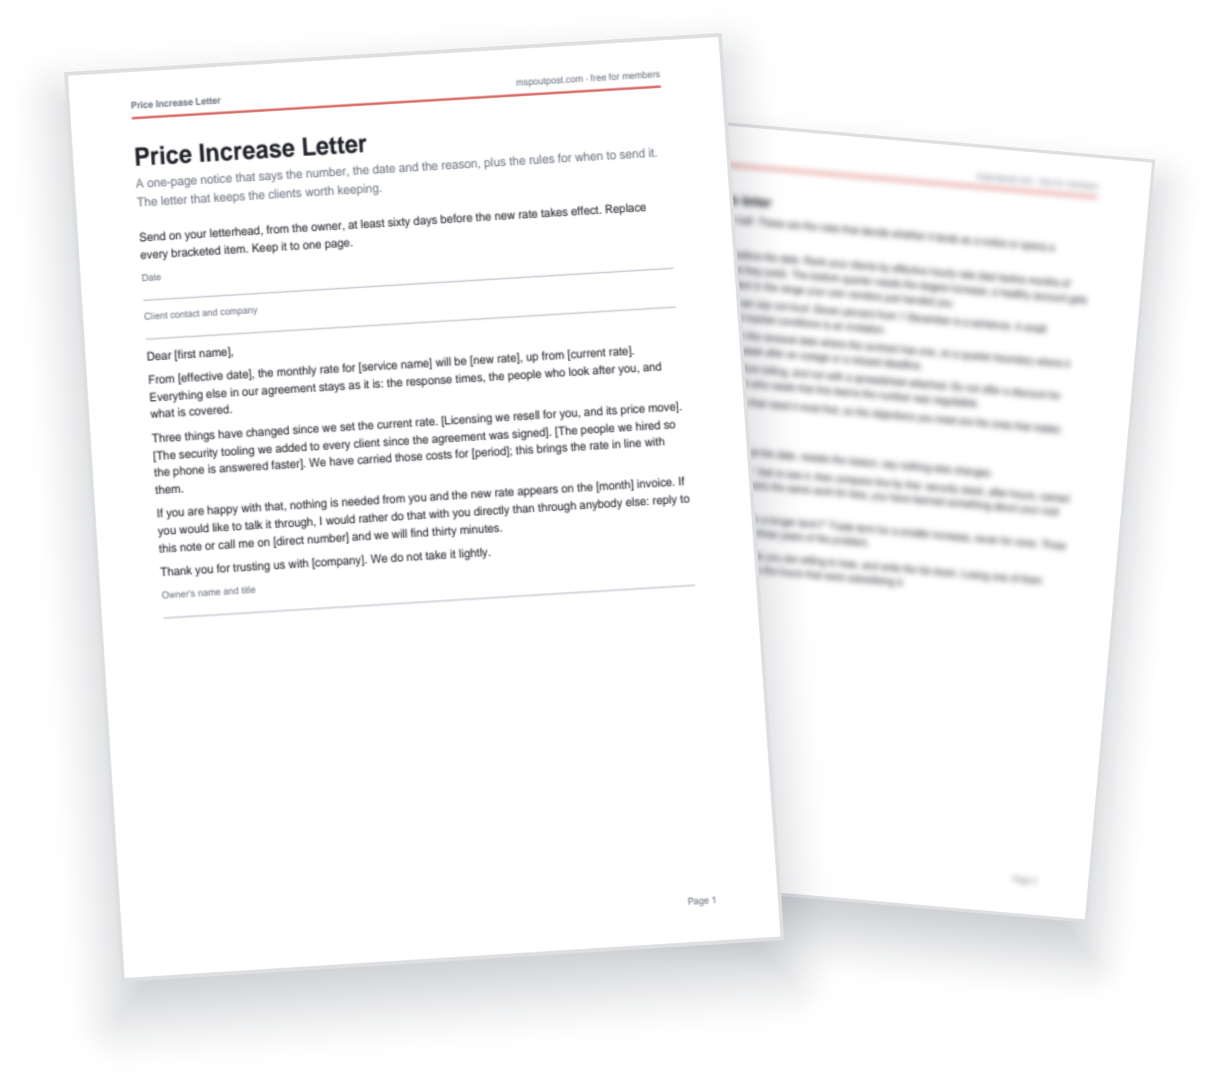
Price Increase Letter
You know your rates are too low. The hard part is the letter. This one says the number, the date and the reason on one page, with the rules for when to send it.
- 2 pages
- Template
- Free with an account
What Is New
Building a Client Onboarding Checklist: 90-Point Technical Onboarding SOP
You sign a new client, hand onboarding to your most reliable tech, and a week later you're untangling a mess: users are calling in because they don't know the…
What One Ticket Really Costs You, and How to Find Out in 30 Minutes
Picture a client who sends a flood of easy requests. Password resets, printer jams, "my Outlook is slow."
The One Sentence That Tells a Prospect Exactly What Your MSP Does
You're at a chamber mixer and someone asks what your MSP does. You launch into the list: IT, security, cloud, help desk, backup, maybe some cabling.